 ProdCanary
Early access · Supabase change lands Oct 30, 2026
Your vibe-coded app works.
Is it safe to ship?
ProdCanary reviews your own Lovable, Bolt or Cursor project for leaked keys, weak Supabase policies, open functions and storage, then hands you a plain-English report and fix prompts you can paste straight into your AI editor.
- Leaked keys in client code
- Weak Supabase RLS policies
- Anon-callable SECURITY DEFINER functions
- Open storage buckets
- Open Firebase rules
- Unauthenticated AI/API routes
Free scan: your top 3 risks in seconds
Upload a .zip of your own project (Lovable, Bolt, Cursor, Next.js, Supabase, Firebase). We review the code statically. We never contact your live site, and we never run your code.
Tip: leave out node_modules, .git, build output and images. Your upload is processed in memory or a temp folder, deleted right after the scan, and never stored. Secrets in results are masked.
RLS is on. That's not the same as secure.
We reviewed 30 public Lovable and Bolt apps built on Supabase. Here's what we found.
service_role key in browser codeSmall sample: n=30 public GitHub repos, reviewed from source. Treat these as directional, not as industry-wide rates.
Heads up: Supabase changes on Oct 30, 2026
New tables in the public schema will no longer be exposed to the Data and GraphQL APIs automatically. When things break, the quick fix is to grant anon broad access, and that can quietly open your data to anyone. ProdCanary flags overly broad grants and policies before you ship them.
How it works
Upload or connect your project
Upload a zip of your project, with GitHub connect coming soon. Read-only, and only your own code.
We review code and config
Client bundles, Supabase migrations and policies, functions, storage, Firebase rules and API routes.
Fix with copy-paste prompts
A plain-English report, ranked by severity, with a fix prompt for Cursor or Lovable on every finding.
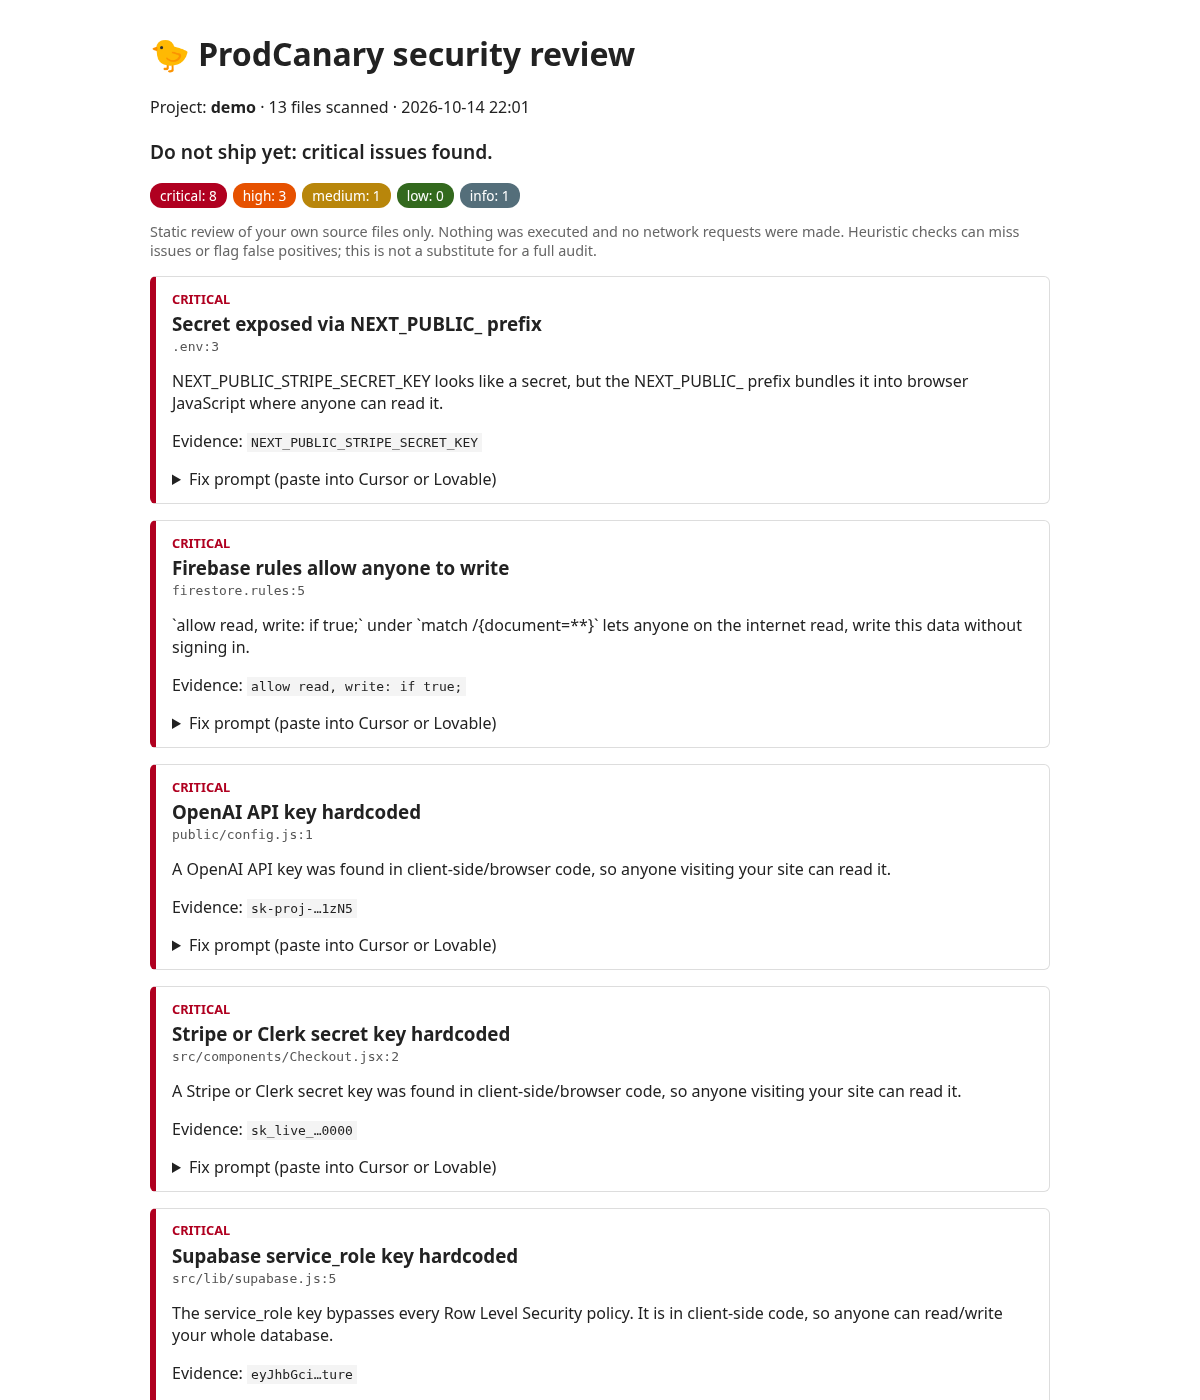
A sample report
Generated from a demo project with deliberately planted flaws. No real app was used.
Pricing
Start free. Pay only if you want every finding and the fix prompts.
Test mode: checkout runs in Stripe's sandbox while we finish setup, so no real charges are made. Use card 4242 4242 4242 4242.
Full report
$29 one-time
- Every finding, explained in plain English
- Copy-paste AI fix prompt for each issue
- Upload the same zip after paying
FAQ
What happens to my code?
ProdCanary reads your code read-only, never modifies it, and deletes it after the scan finishes.
Is this a penetration test?
No. It's an automated review of your source and config. It catches common, high-impact mistakes but doesn't replace a professional pentest or audit.
Do you scan live websites?
No. ProdCanary only reviews projects you upload or connect yourself. It never probes anyone's live site.
Which stacks are supported?
Lovable, Bolt and Cursor-built apps, with a focus on Supabase and Firebase backends and JS/TS frontends.
Will there be false alarms?
Some. We test against real projects to keep them low, and every finding explains why it was flagged so you can judge for yourself.
Ship without the "oh no" moment.
Join the waitlist for early access and launch pricing.
No spam. Unsubscribe anytime.